Your product gets new obligations
The Cyber Resilience Act makes product security a fixed part of development and maintenance. We find where your product falls short and fix it in hardware and firmware, tested on real hardware.
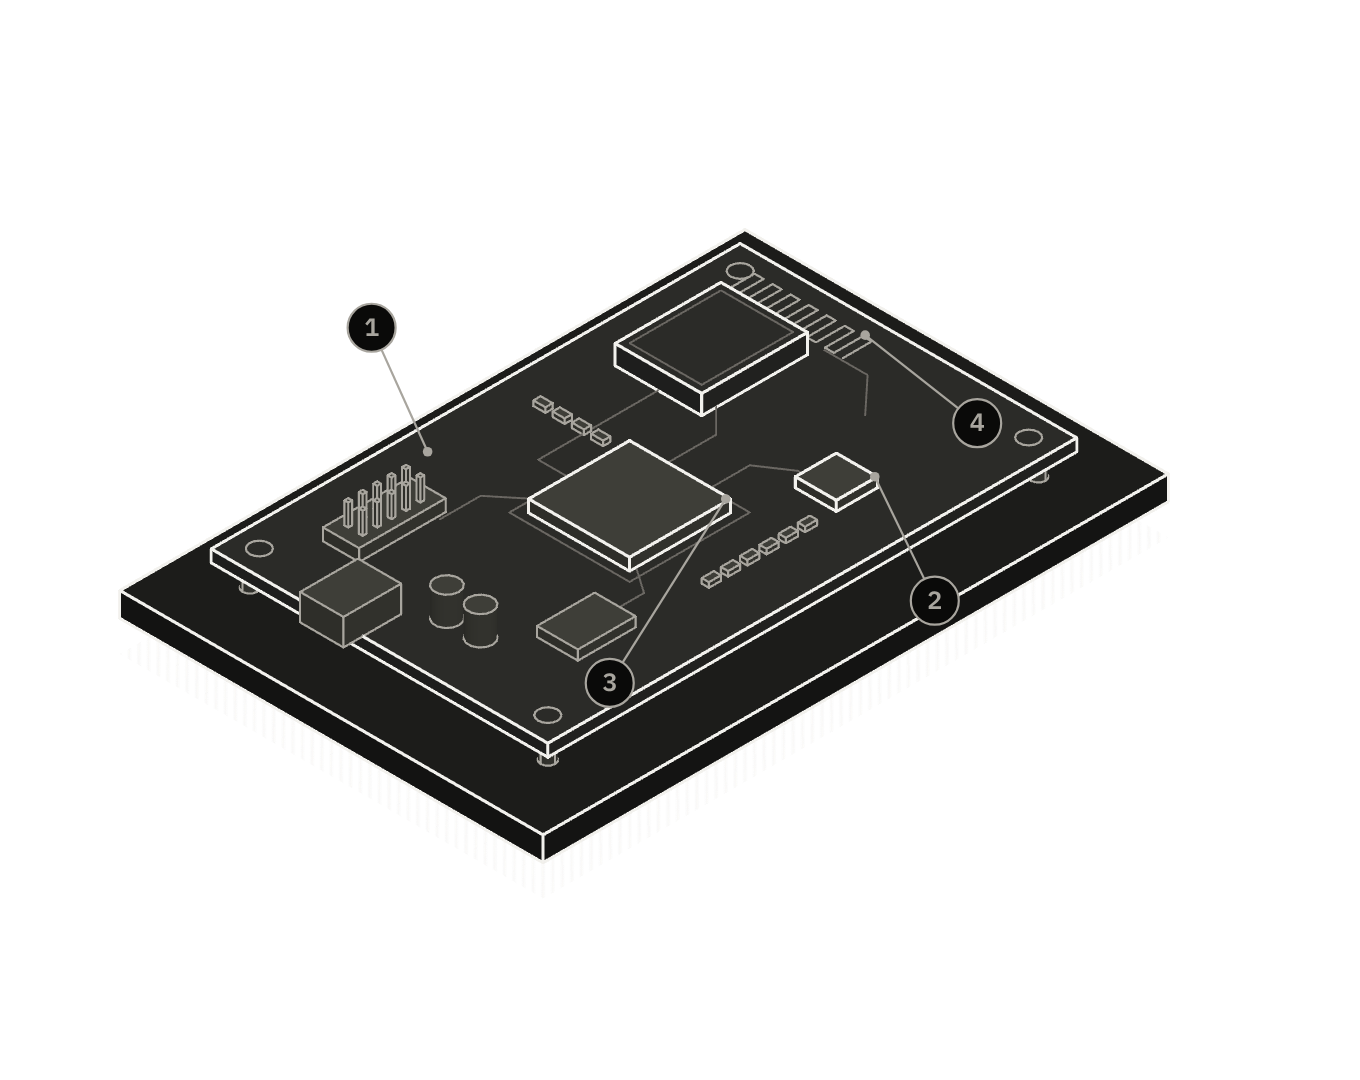
- 1Debug interfaces locked
- 2Secure storage
- 3Secure boot
- 4Signed OTA updates
What the CRA means for your product
If your product has digital elements and is sold in the EU, the CRA most likely applies.
You do not know where your product stands today against the requirements.
Secure boot or signed updates need embedded knowledge you may not have in-house.
The CRA applies in three steps
On 11 Dec 2027.
The CRA enters into force.
Reporting obligation for actively exploited vulnerabilities and severe incidents.
The regulation applies in full.
Source: Regulation (EU) 2024/2847
Which category your product falls into is a legal question, and one for legal advice.
Assess, fix, prove
We review the architecture, the firmware and your processes against the CRA.
We design and implement the measures in hardware and firmware.
We test them on real hardware and follow up after release.
Kilby speeds up, an engineer signs off
Kilby is our AI embedded engineer. He takes over work where that is faster. Experienced engineers decide and sign off on the result.
 Where Kilby helps
- Firmware analysis
- Tests on hardware with every change
- Documentation
- The risk assessment
- The choice of measures
- Validation and release
CRA Readiness Assessment
Know how ready your product is for the CRA.
We review your product against the CRA requirements: architecture, firmware and processes.
Fix the gaps in your product
Measures in hardware and firmware.
We implement the measures from the roadmap and test them on real hardware.
Bring us the hard problem.
A conversation about your problem is the first step.